A treatment center we work with reached out last quarter with a request that captures the most common misunderstanding in this space. Their paid social agency had told them to “just turn on CAPI” to solve their HIPAA exposure.
The implication was that the server-side API was inherently more compliant than the browser pixel.
That is the wrong framing. Turning on Conversions API without the rest of the Meta tracking architecture moves the same protected health information through a different channel.
The exposure stays the same. In some configurations, server-side transmission carries fewer browser-level privacy constraints, which makes the exposure worse rather than better. HHS Office for Civil Rights guidance on tracking technologies applies regardless of which API delivers the event.
Meta does not sign Business Associate Agreements for either the browser pixel or the Conversions API. The compliance does not come from which API the program uses.
The compliance comes from what data the API receives, what BAA-covered intermediary processes it before transmission, and how Event Match Quality is maintained without sending PHI.
CAPI is not a HIPAA solution by itself. The compliance comes from what data is sent, not which API sends it.
Mitch Marowitz, Director of Paid Admissions, Webserv
This guide walks through what Conversions API actually is, why a direct CAPI implementation is not HIPAA-compliant by itself, the three pathways for compliant implementation, and the specific event parameters and Event Match Quality patterns that produce a working setup.
Key Takeaways
- Meta Conversions API (CAPI) is not a HIPAA solution by itself. Meta does not sign Business Associate Agreements for CAPI any more than for the browser pixel. The compliance comes from what data is sent, not which API sends it.
- The recommended implementation pathway routes events through a HIPAA-compliant intermediary platform (Freshpaint, Piwik PRO, Matomo) that signs a BAA, strips PHI from event payloads, and forwards de-identified events to Meta via CAPI on behalf of the advertiser.
- Event parameters are where most CAPI implementations succeed or fail compliance review. URL paths referencing health conditions, custom_data form content, and unhashed user identifiers must always be stripped. Hashed email and phone should only be sent for value-tier conversion events, through a BAA-covered server-side layer, with neutral event names, documented consent, and counsel sign-off.
- Event Match Quality (EMQ) is the trade-off. Compliant treatment center implementations usually score lower than non-regulated verticals, and chasing a higher score by adding identifiers or page context is how programs create compliance exposure.
What Conversions API actually is
Conversions API (CAPI) is Meta’s official server-side tracking pathway. It exists in part because the browser pixel has become unreliable across iOS privacy updates and ad blockers, and in part because server-side tracking gives advertisers more control over what data is transmitted to Meta.
The technical mechanics are straightforward. The advertiser’s server (or a third-party service) sends conversion event data to Meta’s CAPI endpoint via a structured POST request.
The payload includes the event name, the event timestamp, and a set of user identifiers that Meta uses to match the event to a Facebook or Instagram user.
The user identifier set is what makes the architecture sensitive. CAPI accepts hashed email, hashed phone, hashed first name, hashed last name, IP address, user agent, click ID (fbc), and browser ID (fbp).
Meta uses these to construct an Event Match Quality (EMQ) score that determines how reliably the event is attributed to a known user.
Hashing is one-way, but a hashed identifier paired with a behavioral health context can still be PHI. Hashing alone does not make a direct transmission compliant; the identifier has to pass through a BAA-covered layer that strips everything else first.
Why CAPI alone is not a HIPAA solution
MOST COMMON MISUNDERSTANDING
Deploying Meta Conversions API on the assumption that server-side signals automatically clear HIPAA. They do not. CAPI moves the tracking off the browser and eliminates cookie fragility, but the payload can still contain PHI if the implementation sends form fields, IP addresses, or user identifiers directly to Meta. A HIPAA-compliant CAPI setup requires a HIPAA-aware intermediary layer that strips or hashes protected fields before the event ever leaves your infrastructure — otherwise you are shipping the same violation with cleaner plumbing.
Three specific compliance issues persist with a direct CAPI implementation that is not routed through a HIPAA-compliant intermediary.
Meta still does not have a BAA in place. The Conversions API is a Meta product. Meta has not signed Business Associate Agreements for any of its advertising APIs, and there is no current path to obtain one.
A treatment center sending event data directly to Meta’s CAPI endpoint is sending regulated data to a non-covered entity. The HIPAA exposure is identical to the browser pixel exposure.
Event parameters can carry PHI. A direct CAPI implementation that sends URL paths in the event_source_url parameter or page-context data in custom_data fields is transmitting the same PHI as a browser pixel firing on a behavioral health page. The transmission method changed. The data did not.
User parameters carry PHI when combined with health context. Hashed email and hashed phone are PHI in the context of a substance use disorder treatment center. The hashing is reversible at scale by anyone with access to enough source data.
More importantly, the combination of a hashed identifier with the implicit context (this user converted on a treatment center site) is itself protected health information.
The compliant pattern requires that PHI never reach Meta in the first place, regardless of which API delivers the event.
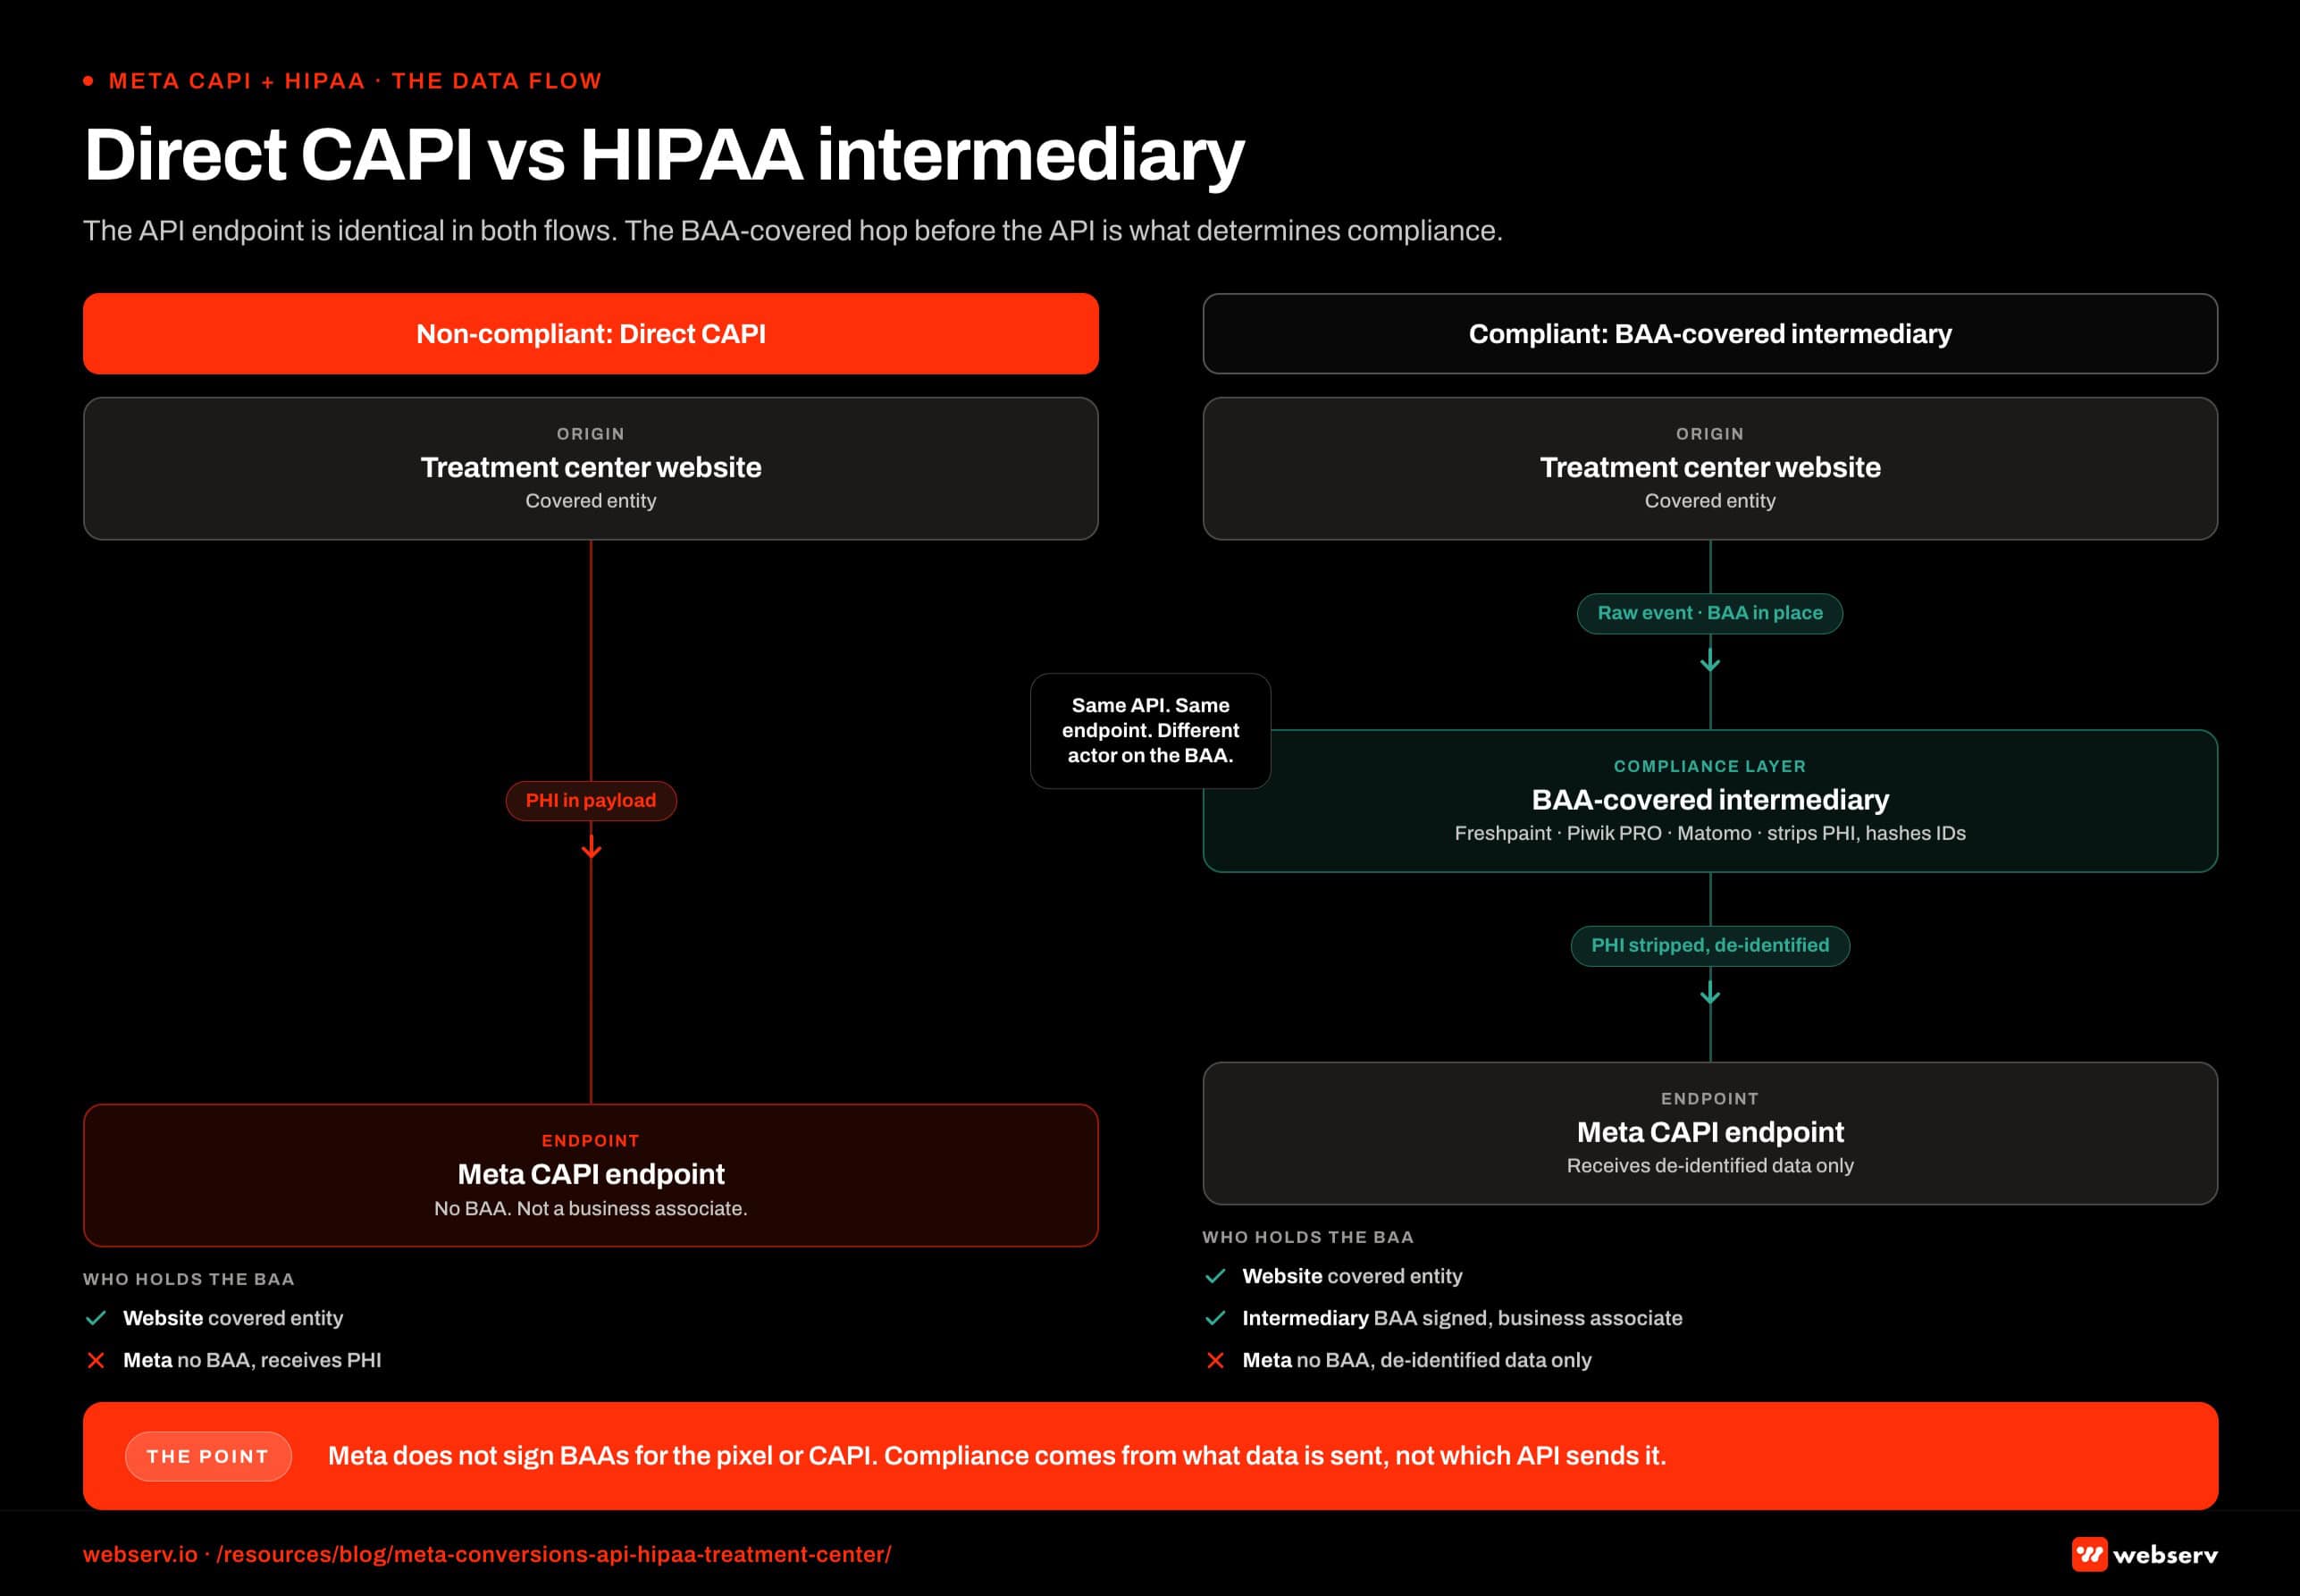 Infographic titled ‘Direct CAPI vs. HIPAA intermediary’.
The three implementation pathways
Three implementation pathways exist for CAPI in a HIPAA-compliant treatment center setup. Each has trade-offs, and they parallel the same architecture decisions on the Google Ads side of conversion tracking.
Pathway 1: HIPAA-compliant intermediary platform. This is the recommended pathway for almost every treatment center.
Platforms like Freshpaint, Piwik PRO, and Matomo sign BAAs and operate as a server-side intermediary that ingests conversion events from the website, strips PHI, and forwards de-identified events to Meta via CAPI.
The platform handles event hashing, parameter mapping, and deduplication on behalf of the advertiser. Platform fees vary by vendor and event volume, so get quotes that include the BAA.
Pathway 2: Server-side Google Tag Manager with custom logic. A custom server-side GTM container can be configured to intercept conversion events, strip PHI, and forward to Meta via CAPI.
The setup requires engineering work, including custom server-side templates, parameter scrubbing logic, and deduplication handling. Expect several weeks of engineering time to build it correctly.
The ongoing maintenance cost is real because Meta updates CAPI specs regularly.
Pathway 3: Fully custom server-side implementation. A development team can build a custom server that receives website events, processes them, and transmits to Meta via CAPI directly. The pathway is technically valid.
It is also rarely worth the engineering investment for a single-platform paid social account. Custom builds are common at programs that have engineering teams already managing other infrastructure and that want to centralize event handling across multiple advertising platforms.
For most treatment centers, Pathway 1 is the right choice. The HIPAA intermediary platform is a known, validated solution that integrates with the rest of the marketing stack. The other pathways exist for programs with specific engineering needs that the standard platforms do not meet.
How the HIPAA intermediary pathway actually works
The implementation through a HIPAA-compliant intermediary follows a consistent pattern across vendors.
Step one: install the intermediary’s tracking script on the website. The script replaces the browser-side Meta pixel. The script collects event data in the same way the pixel did, but transmits it to the intermediary’s BAA-covered infrastructure rather than to Meta directly.
Step two: configure event mapping. Inside the intermediary’s interface, map each website event (page view, form submission, phone click) to its corresponding Meta CAPI event. Standard events like Lead, ViewContent, and Contact map cleanly. Custom events require deliberate mapping decisions, which is where most implementation errors happen.
Step three: define what data is forwarded versus stripped. The intermediary’s PHI handling rules need to be configured deliberately. URL paths that reference health conditions get stripped.
IP addresses get either hashed or removed depending on the intermediary’s BAA terms. Form field content is never forwarded. The configuration is the compliance layer, and it has to be reviewed by someone who understands HIPAA.
Step four: connect the intermediary to Meta via CAPI. The intermediary handles the actual server-to-server transmission to Meta. The advertiser provides Meta credentials (Pixel ID and access token) and the intermediary builds the CAPI payload using the de-identified event data.
Step five: validate the implementation through Meta’s Events Manager. Meta provides a CAPI test mode that shows incoming events without affecting attribution. Use the test mode to confirm that the events Meta is receiving contain only de-identified data and that no PHI is appearing in the payload.
Programs with cooperative IT and a clean website move fastest. Programs with years of accumulated tracking take longer, because cleaning up the existing pixel implementation runs alongside the new build.
Event parameters: what to send and what to strip
The event parameter layer is where most CAPI implementations succeed or fail compliance review.
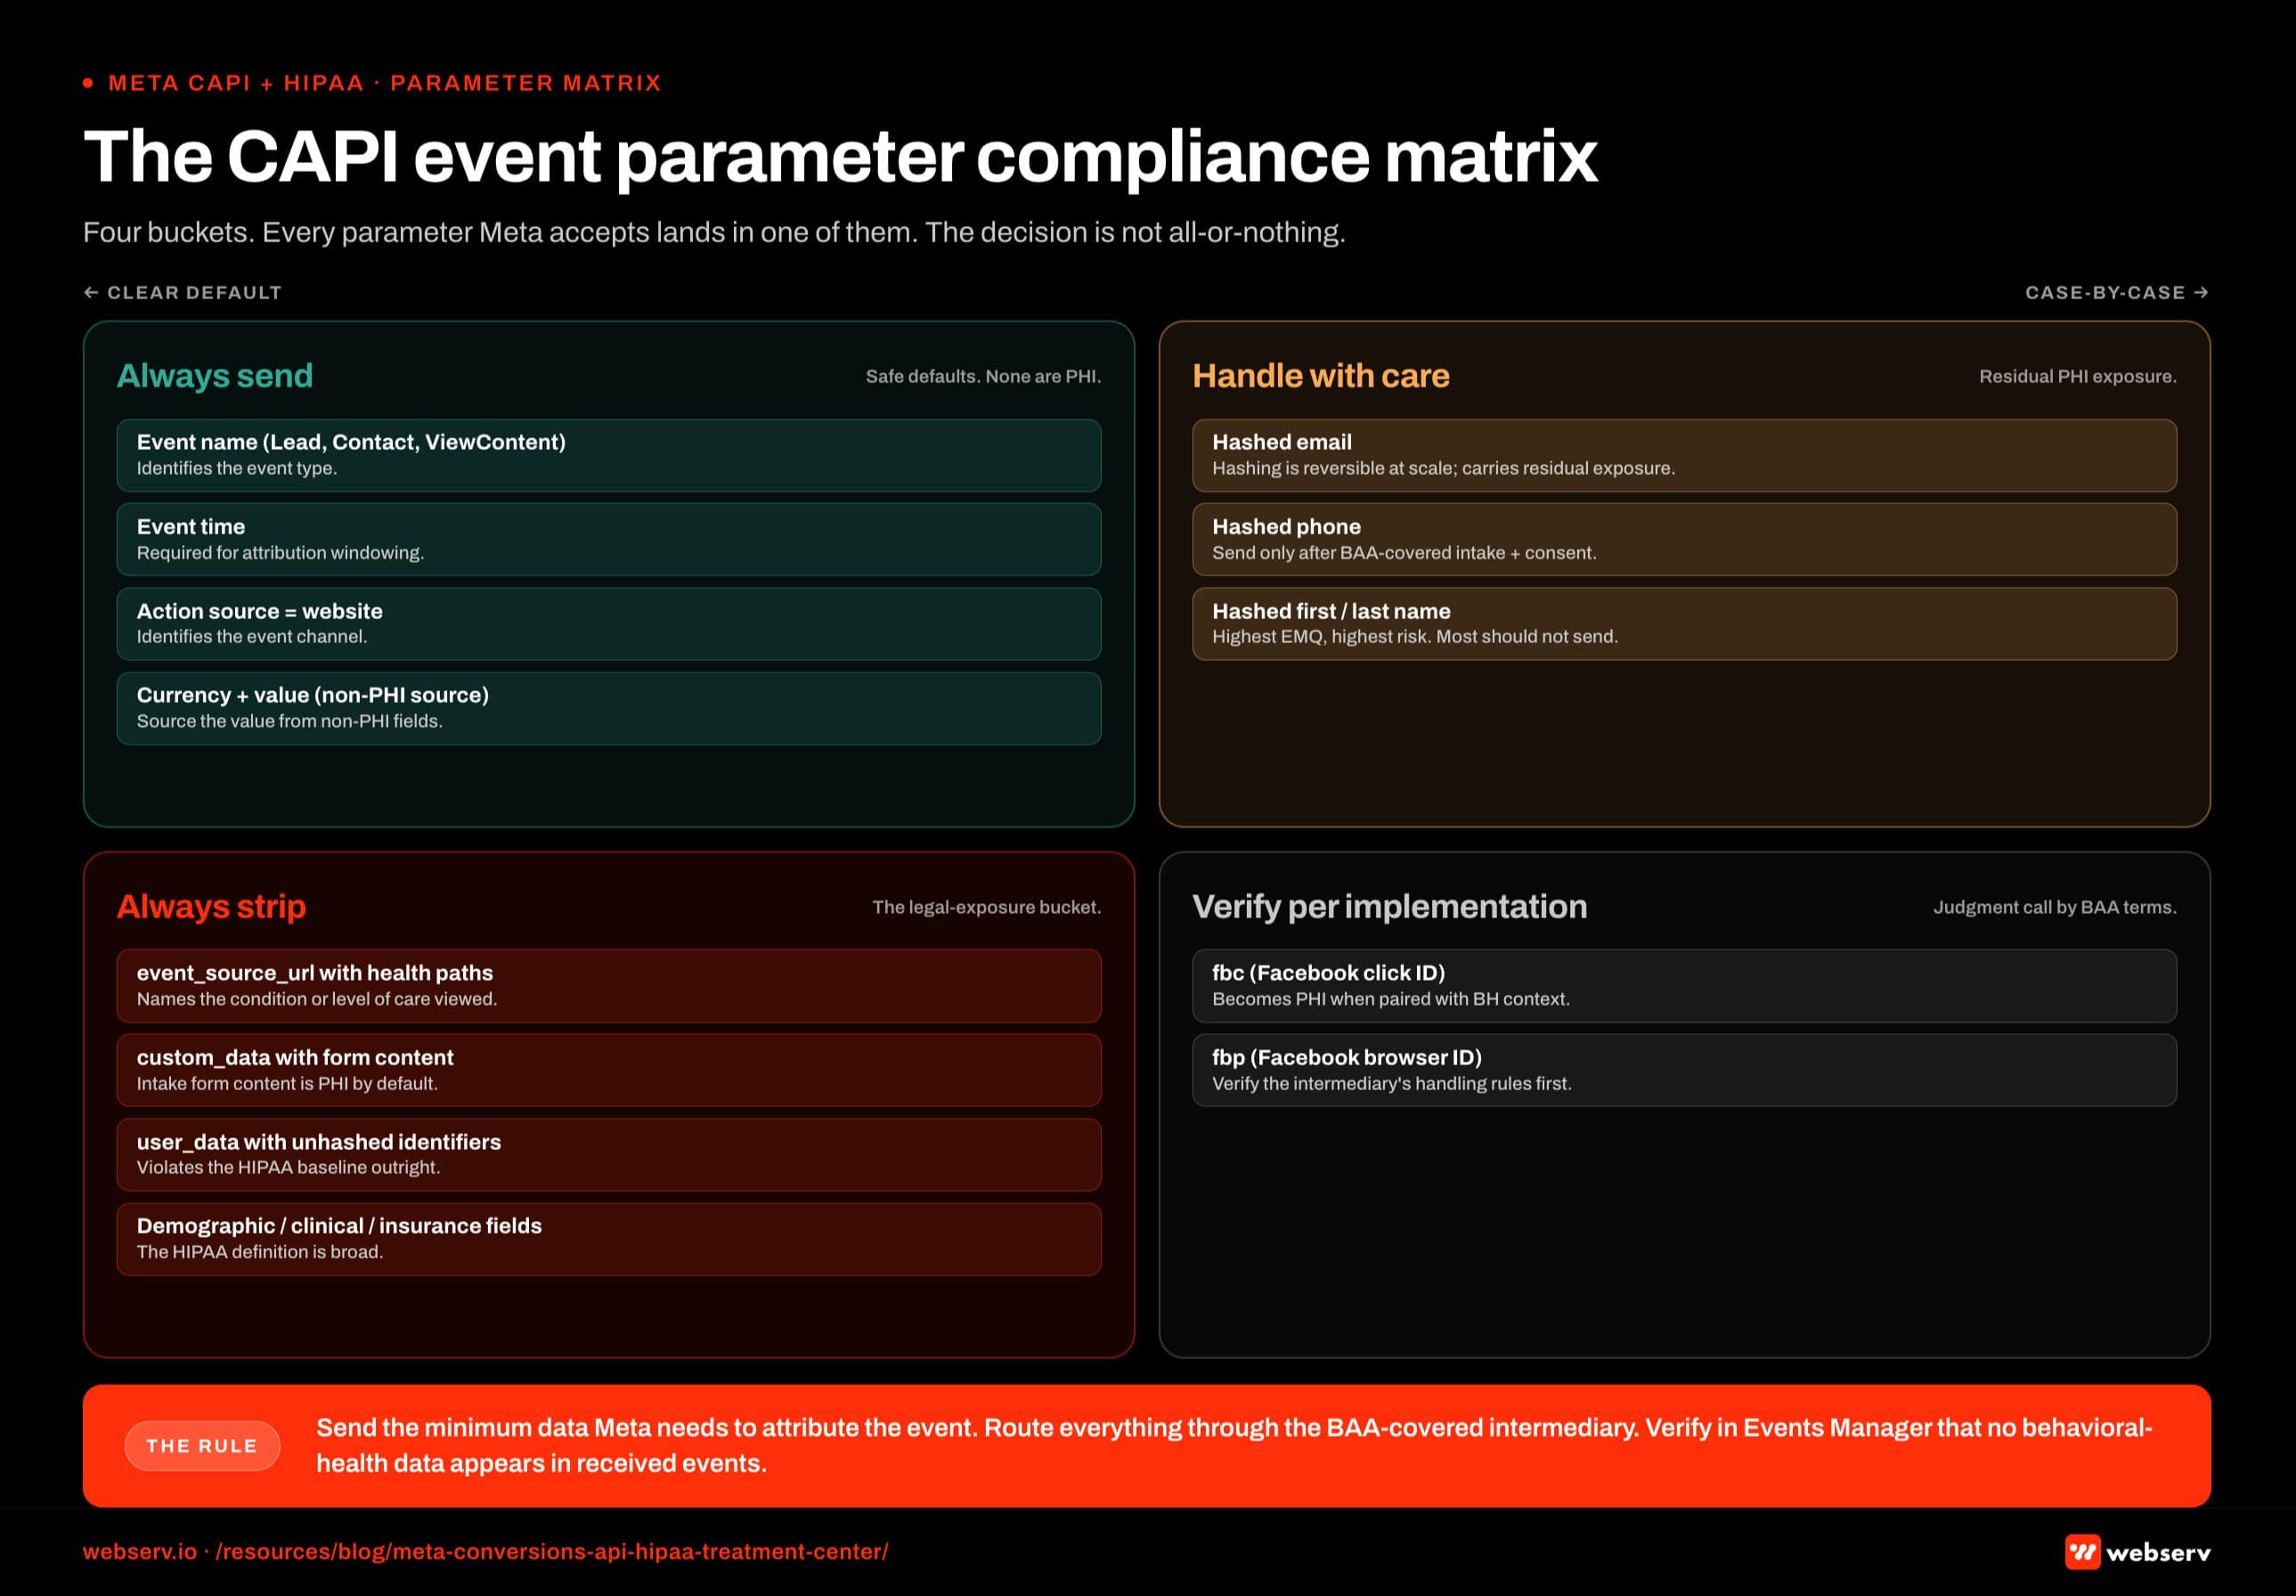 Infographic titled ‘The CAPI event parameter compliance matrix’.
Server-side parameters that should be transmitted. Event name (Lead, Contact, ViewContent, etc.). Event time. Hashed click ID (fbc) when available. Hashed browser ID (fbp) when available. Action source set to “website.” Currency and value when applicable, calculated from non-PHI sources.
User parameters that need careful handling. Hashed email and hashed phone are technically supported by CAPI but carry the PHI exposure described earlier.
The compliant pattern hashes only after the email or phone has been collected via a BAA-covered intake form, and forwards the hash only with the patient’s documented consent and your compliance counsel’s sign-off.
Limit identifiers to value-tier conversion events (admit, VOB completed, scheduled admission) sent through the BAA-covered layer with neutral names such as tier_1_conversion, as laid out in our HIPAA-safe conversion tracking stack. Never attach condition, level of care, or admit date to the identifier, and never use descriptive event names: the FTC’s 2024 action against Monument turned on events like “Paid: Weekly Therapy” sent alongside user identifiers.
Parameters that should always be stripped before transmission. event_source_url containing health-condition paths. custom_data fields containing form content. user_data fields containing unhashed identifiers. Any parameter that encodes patient demographic, clinical, or insurance information.
Parameters that need verification on every implementation. The fbc and fbp parameters are not PHI by default, but they become PHI when paired with a behavioral health context.
Their inclusion is a judgment call that depends on the program’s HIPAA risk tolerance and the BAA terms with the intermediary platform.
The general rule: send the minimum data required for Meta to attribute the event, route everything through the BAA-covered intermediary, and verify in Meta’s Events Manager that no behavioral-health-specific data is appearing in the received events.
Event Match Quality without PHI
Event Match Quality (EMQ) is Meta’s score for how reliably an event can be attributed to a known Facebook or Instagram user. Higher EMQ correlates with better campaign optimization. Standard CAPI implementations target EMQ scores of 7 or higher on Meta’s 1-to-10 scale.
Treatment center implementations that strip PHI from event payloads typically operate at lower EMQ than non-regulated verticals. The trade-off is real. The mitigation is also real.
EMQ levers that work without transmitting PHI. Click ID (fbc) and browser ID (fbp) when available add meaningful EMQ without adding PHI exposure. Action source and event source both contribute. Event timestamp accuracy matters. Adding these parameters consistently raises EMQ even without user-identifier data.
EMQ levers that involve user identifiers. Hashed email and hashed phone are among the highest-impact EMQ contributors. Send them only for value-tier events through the BAA-covered layer, with consent and counsel sign-off. Skip hashed names entirely.
The practical EMQ expectation for treatment centers. Programs that strip PHI score lower than unregulated advertisers, and that is an acceptable cost.
Campaigns can still optimize well on a lower score when the value-tier events tell Meta which conversions matter.
The EMQ trade-off is a choice between optimization performance and compliance exposure. Do not raise the score by adding identifiers, page context, or descriptive event names, which is how accounts land in the suspension or audit category.
How Profound Treatment drove 31 admits and a 42% drop in cost per viable in one quarter
Broad match pivot, negative keyword management, and intake-level conversion tracking turned a fragmented paid strategy into a predictable admissions engine.
Read the case study →68 viable VOBs at $4,529 cost per viable
Browser pixel deduplication
Programs that run both the browser pixel and CAPI in parallel need to handle event deduplication. Meta uses event_id and event_name combinations to identify duplicate events arriving from both pathways and counts them only once.
The deduplication logic requires consistent event_id generation across both transmission methods. The intermediary platform handles this when configured correctly. Direct implementations need to assign event IDs in the website code and pass them through both the pixel and the CAPI payload.
The compliant pattern for treatment centers is usually to remove the browser pixel entirely and rely on CAPI through the intermediary. This eliminates the deduplication concern and removes a potential PHI transmission pathway in one decision.
Some implementations keep a stripped-down browser pixel for Meta’s automated event matching, but only after the pixel has been audited to confirm it is not transmitting URL paths or form content. Audit each page with browser network tools. The audit is not optional.
Testing and verification
Three verification steps confirm that a CAPI implementation is operating compliantly.
Verification one: Meta Events Manager test mode. In the Events Manager, enable test events for the relevant Pixel ID. Trigger conversions on the live website.
Confirm that the events Meta receives contain only the de-identified parameters described above. Specifically check the event_source_url field and any custom_data or user_data parameters for PHI leakage.
Verification two: browser network tab review. Open Chrome DevTools or Firefox Developer Tools, go to the Network tab, and load behavioral-health-specific pages on the website.
Filter the network traffic for facebook.com and meta.com endpoints. Confirm that no traffic is going directly to Meta with PHI in the payload. If the implementation is correct, the only Meta-bound traffic should be from the HIPAA-compliant intermediary.
Verification three: intermediary platform audit. Log into the HIPAA-compliant intermediary platform and review the events being forwarded to Meta.
Most platforms provide a log or dashboard showing the exact payload structure of outgoing CAPI events. Verify that the payload structure matches the compliance specification and that no PHI is being transmitted.
These verification steps should be performed on initial implementation and quarterly thereafter, because tracking implementations drift over time, especially when websites are updated, agencies change, or new platforms are added to the marketing stack. Quarterly verification catches drift before it accumulates into compliance exposure.
What to ask your paid social partner this week
Three questions surface whether a paid social partner is operating with a HIPAA-compliant CAPI implementation. Ask all three.
First, ask whether the program’s CAPI implementation routes through a HIPAA-compliant intermediary platform with a signed BAA. If the answer is “we send events to Meta directly through the API” or “we use server-side GTM without BAA coverage,” the setup is non-compliant.
Second, ask the partner to demonstrate the event payload that Meta is currently receiving. If the partner cannot pull a sample event payload from the Events Manager test mode, they are not operating with the visibility a compliant setup requires.
Third, ask what user_data parameters the implementation sends. If the answer includes hashed email or hashed phone, ask to see the BAA, the consent language, the neutral event names, and the counsel sign-off. Without all four, turn the identifiers off.
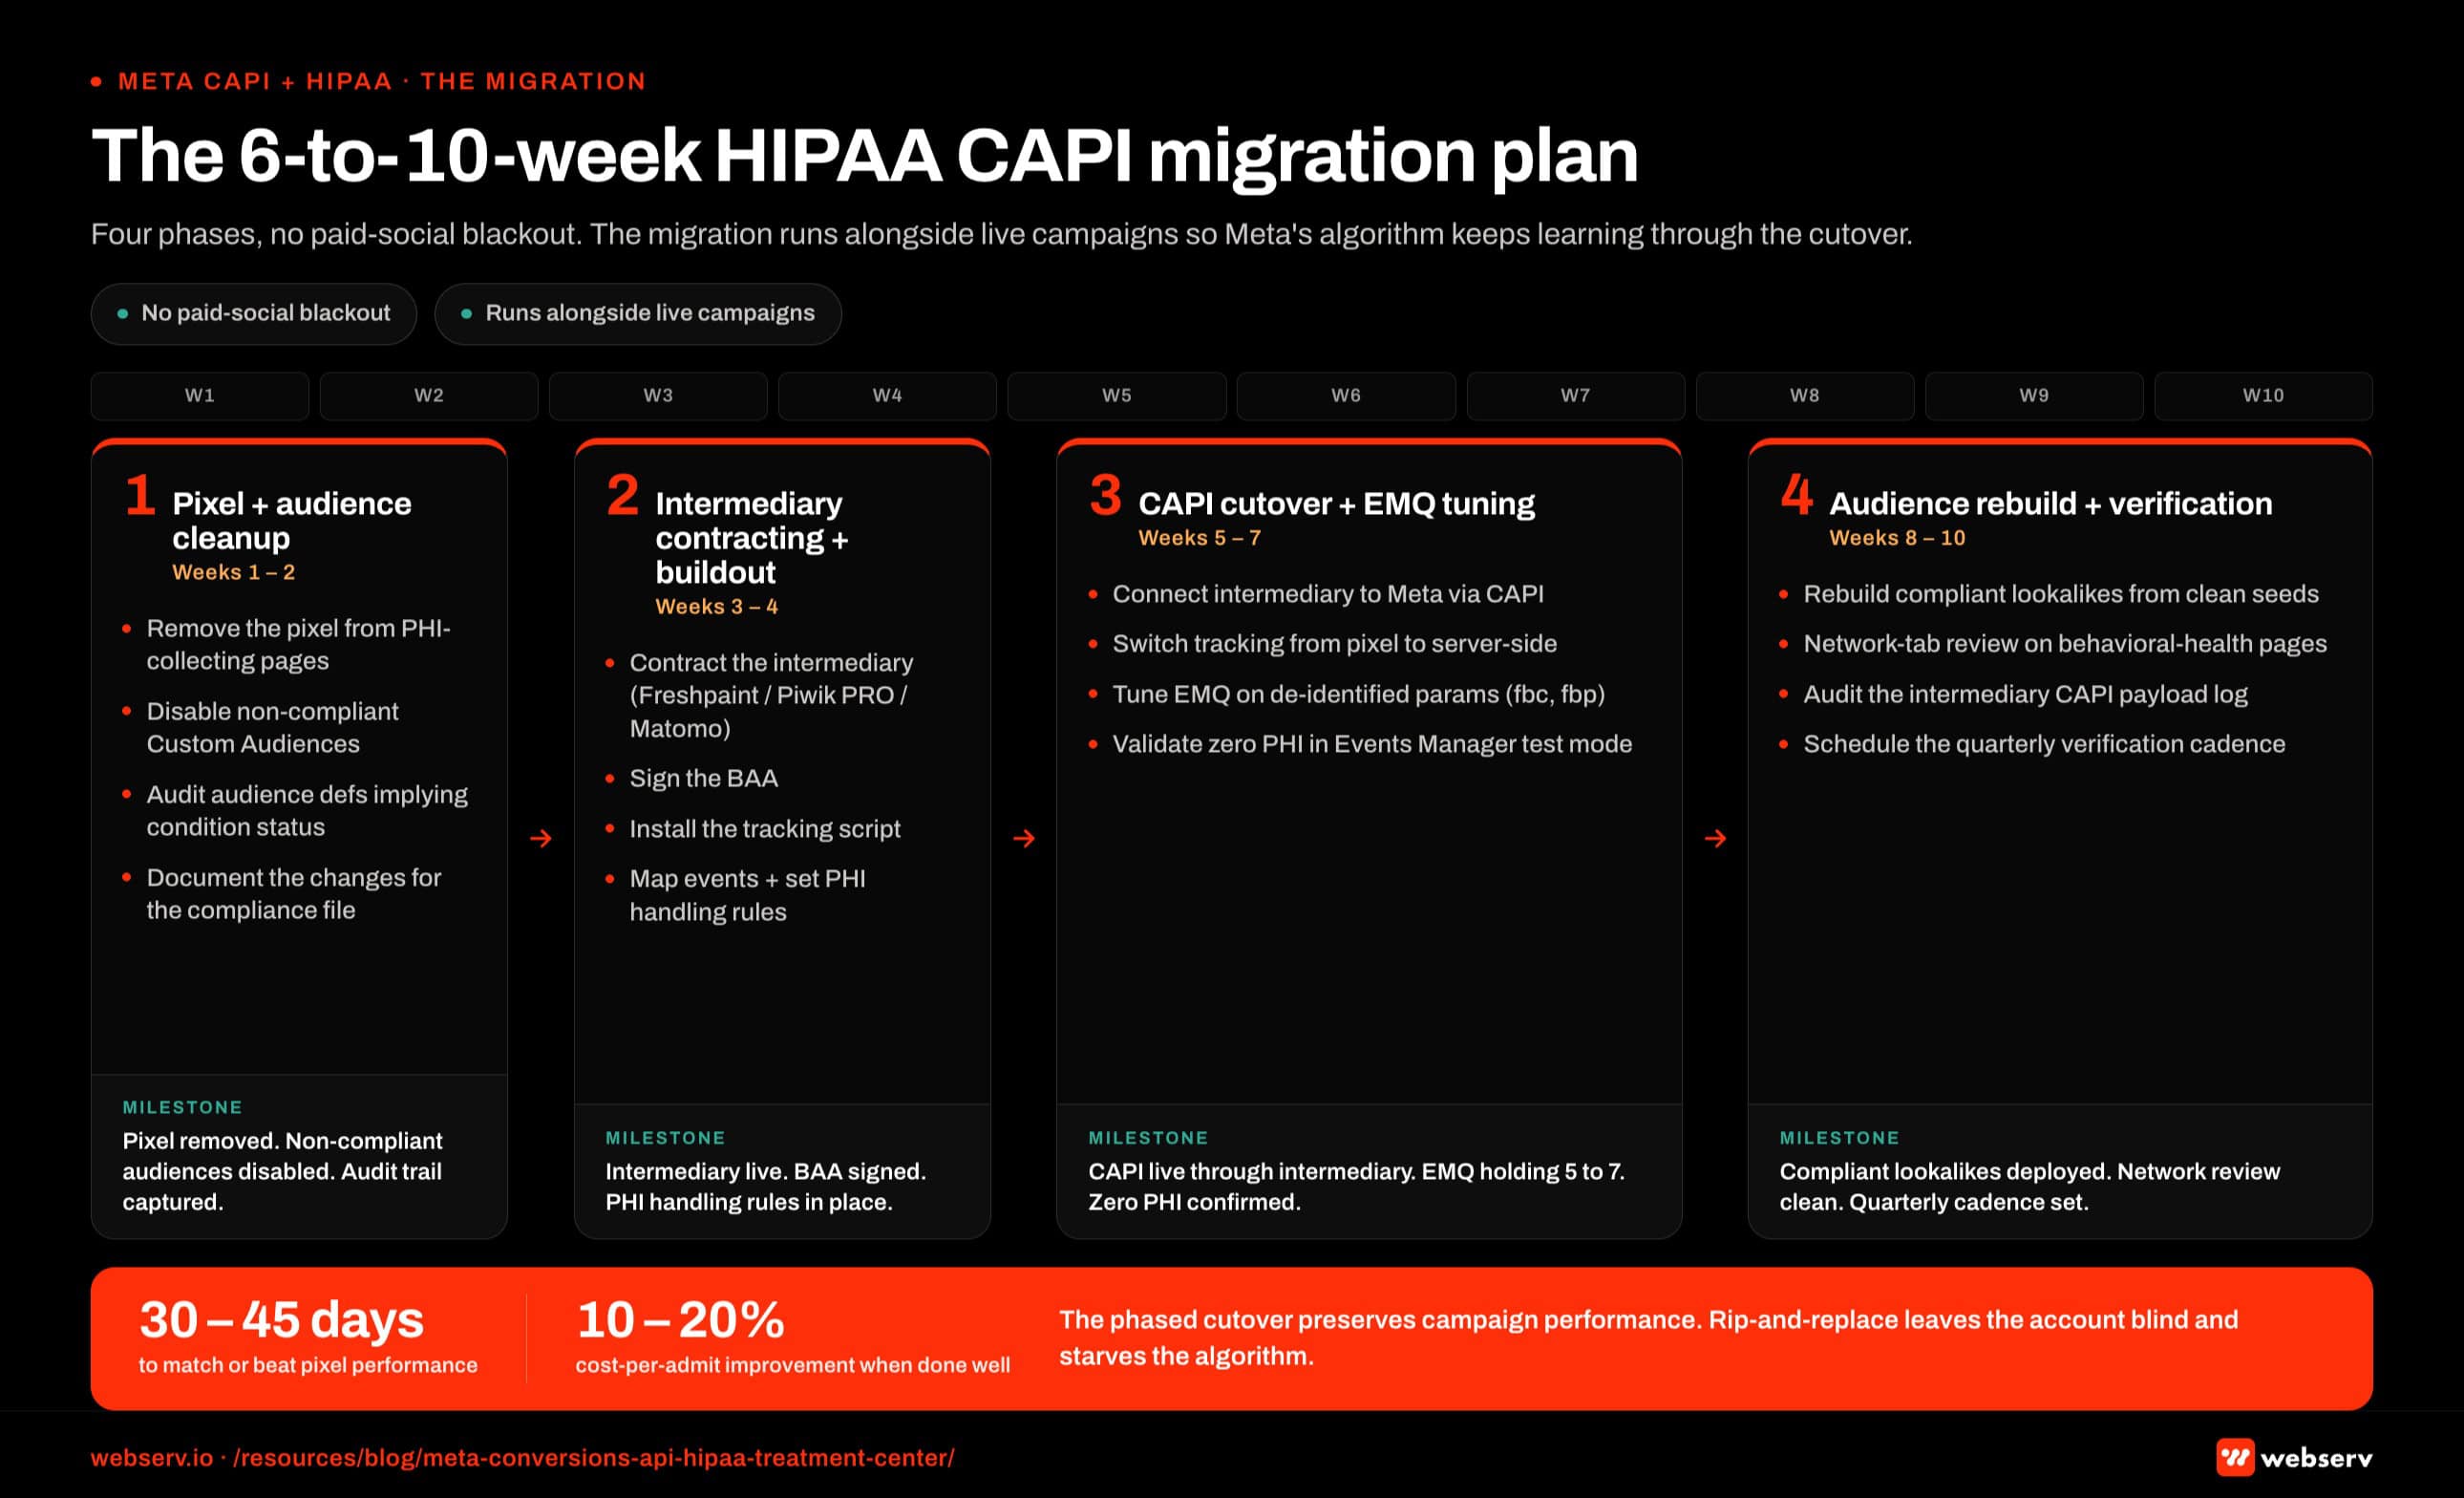 Infographic titled ‘The 6-to-10-week HIPAA CAPI migration plan’.
CAPI is the right pathway for treatment center Meta advertising. The implementation pattern that produces a compliant setup is specific.
The shortcut version that just enables CAPI in Meta’s interface and assumes the rest is handled produces the same legal exposure as the browser pixel did, with a cleaner-looking interface obscuring the underlying problem.
The fix is closeable in a quarter, and the foundation it builds is what every other Meta advertising optimization gets to stand on. For the wider Meta picture, see our guide to social advertising for treatment centers, and for how paid fits the rest of the program, our behavioral health marketing guide. Operators who want a head-start on identifying which paid social agencies actually run this stack can work from our scored shortlist of behavioral health firms with documented BAA-covered CAPI implementations.
Meta Ads Policy and Audiences Without Patient Data
What Meta itself requires (Health & Wellness policy)
Meta operates a separate compliance layer through its Health & Wellness policy, and the policy applies to advertisers in healthcare verticals and adds restrictions beyond what HIPAA requires.
The policy restricts targeting. Treatment center advertisers cannot use sensitive-category targeting or audience segments that proxy health conditions. This overlaps with HIPAA but is enforced separately by Meta’s automated systems.
The policy restricts ad creative. Before-and-after content is prohibited across all healthcare verticals. Direct claims about treatment outcomes require substantiation. Fear-based messaging that exploits emotional distress is restricted.
The policy restricts audience composition. Custom Audiences uploaded from patient or inquiry data trigger Meta’s sensitive-category detection. Once flagged, the audience is restricted from use in campaigns and the account picks up a strike that compounds over time.
The policy operates alongside LegitScript certification. LegitScript is the gating credential. The Health & Wellness policy is the ongoing compliance layer that determines whether ads continue running once the program is certified. The LegitScript application process runs in parallel with the Meta tracking architecture work; both should be active before scaling spend.
Step 3: Audience strategy without patient data
The audience layer is where most behavioral health Meta accounts go non-compliant. Standard paid social practice for ecommerce involves uploading customer lists, building Lookalikes, and running retargeting against site visitors.
In behavioral health, the standard playbook does not apply. The compliant audience strategy has three components.
Broad geographic and demographic targeting. The campaign targets adults in the geographic markets the program serves. No health-condition affinity layering. No in-market segments related to addiction or mental health. No demographic combinations that proxy a sensitive category.
Lookalike audiences seeded on non-PHI sources only. Standard Meta Lookalikes are typically seeded on uploaded customer lists or pixel-defined remarketing audiences. In a HIPAA-compliant treatment center setup, neither source is available. The Lookalike has to be seeded on something else, such as engagement audiences (people who interacted with Facebook or Instagram content) or non-sensitive website actions captured through the HIPAA-compliant intermediary.
No uploaded patient or inquiry lists. This is the hardest constraint for marketing teams to accept. Uploading a CSV of past patients or inquiry data to Meta is a clear HIPAA violation. It is also against Meta’s own Health & Wellness policy. The temptation to upload anyway is real because Lookalikes seeded on patient data tend to perform well. The exposure is not worth it.
Engagement-based retargeting only. Meta allows retargeting based on engagement with Facebook and Instagram content (people who watched a video, engaged with a post, etc.). This engagement data lives within Meta’s platform and does not implicate the program’s HIPAA exposure. It is the only retargeting layer most treatment centers should be using.
The constraint produces lower precision targeting than what is possible in a non-regulated vertical. The trade-off is that the campaigns run cleanly and the program is not building a legal liability that compounds over time.
Google Ads and GA4: The Rest of the Tracking Stack
The value-tier conversion event architecture
The single most consequential configuration decision in the stack is how conversion events get structured. Get this wrong and every downstream optimization runs against the wrong signal.
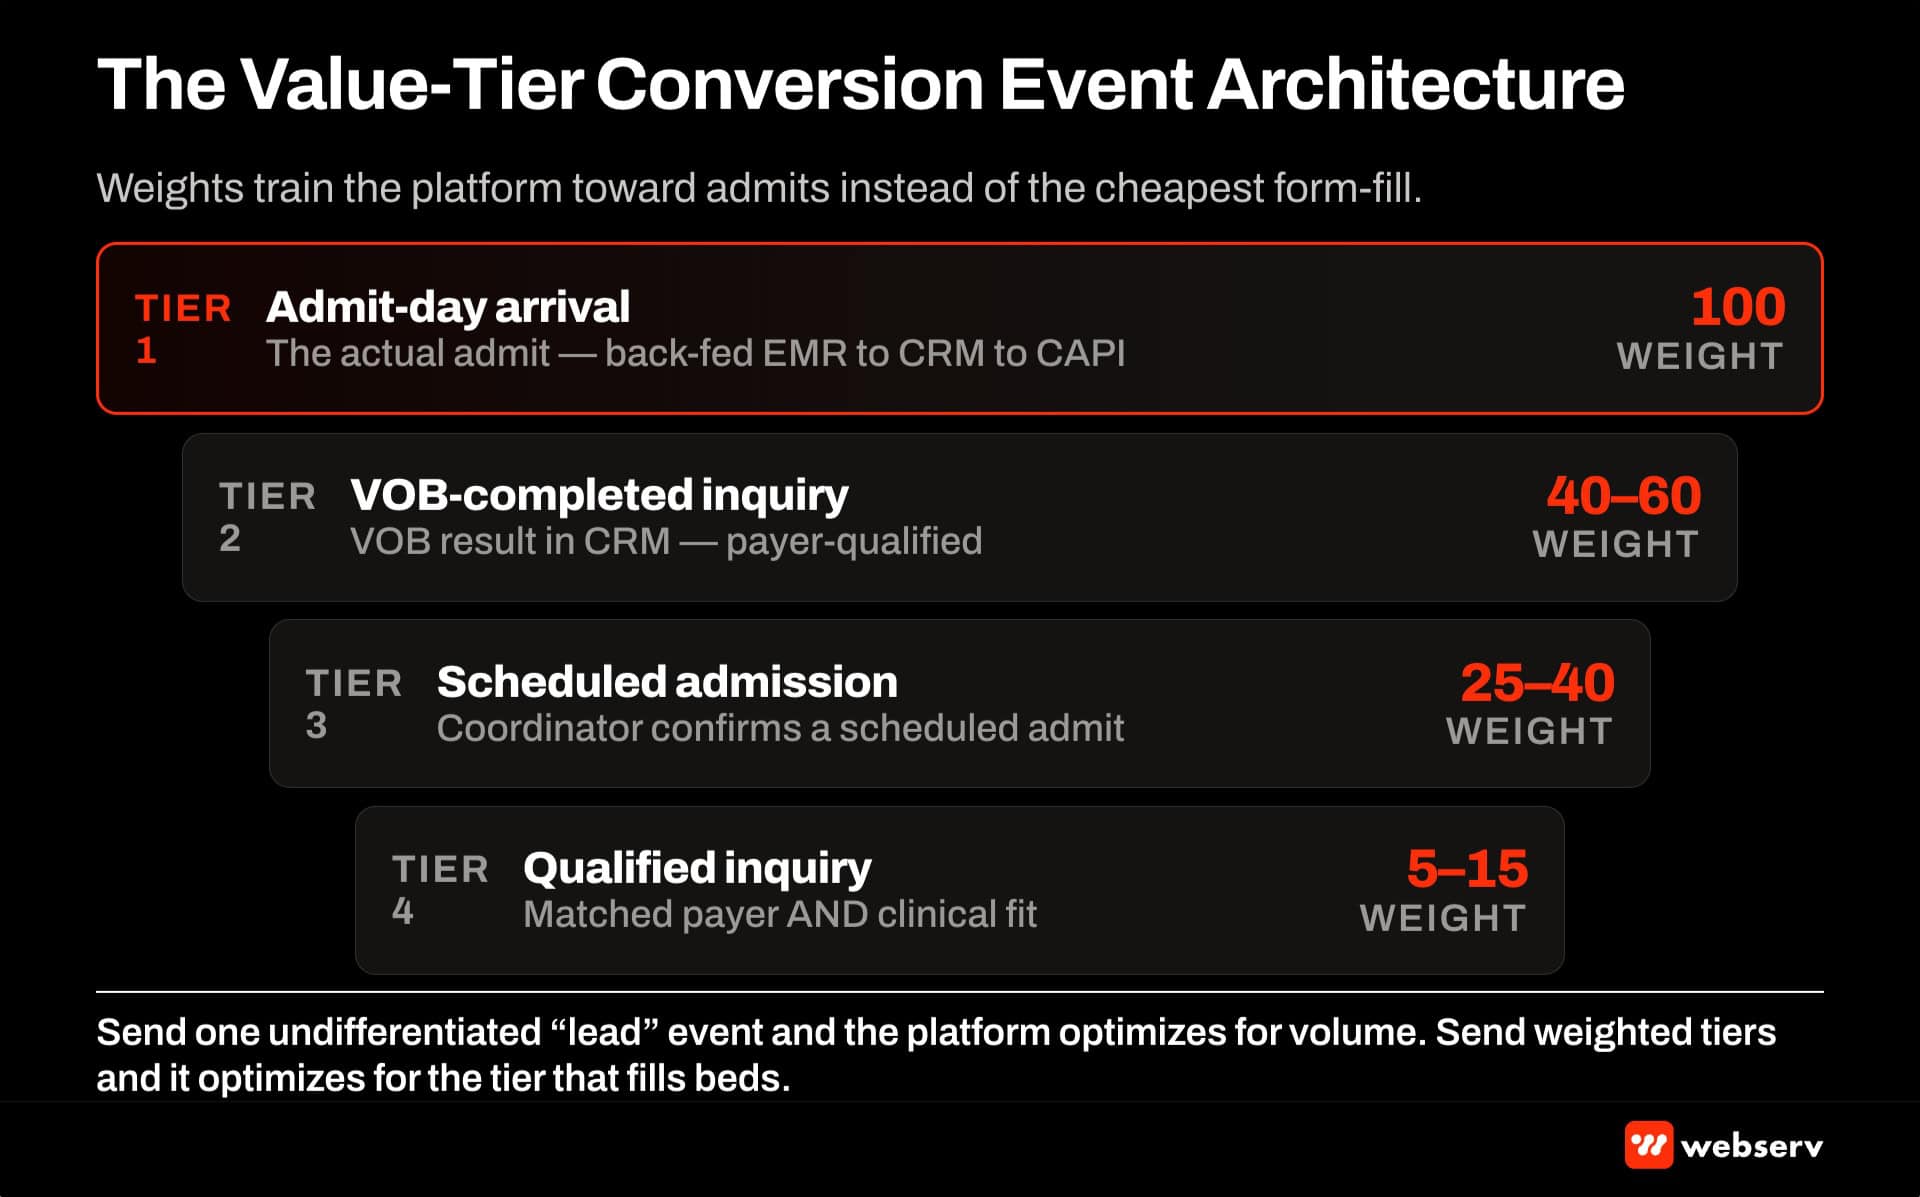
Four tiers, ranked by value to the treatment center.
Tier 1: Admit-day arrival
The patient physically arrives at the facility for admission. This is the highest-value conversion because it is the point at which reimbursement becomes possible. Value: the facility’s average revenue per admit (adjusted for payer mix). Pull it from the facility’s own billing data rather than an industry average.
Tier 2: VOB-completed inquiry
The family has provided insurance information, VOB has run successfully, and the plan qualifies for admission. This is a leading indicator of Tier 1. Value: a fraction of Tier 1, set from the facility’s own VOB-to-admit conversion rate.
Tier 3: Scheduled admission
The family has scheduled an admit day but has not yet arrived. Value: a fraction of Tier 1, set from the facility’s own no-show rate.
Tier 4: Qualified inquiry
The family has completed a form or a call that meets the qualification criteria (in-market, insurance profile viable, family decision-maker engaged) but has not yet completed VOB. Value: small, typically 5 to 10 percent of Tier 1.
Form-fills without qualification, brochure downloads, and general newsletter signups do not qualify as conversion events for AI-optimized campaign purposes. Feeding those into Meta CAPI or Google Ads as conversions produces the signal contamination that breaks AI Max and Advantage+.
The four tiers get transmitted with specific value fields set in the conversion event payload. AI Max and Advantage+ use those value fields to optimize toward the higher-value conversions.
When the value tiers are set correctly, the algorithms pursue Tier 1 and Tier 2 conversions preferentially. When they are missing or misconfigured, the algorithms chase Tier 4 form-fills at the expense of Tier 1 admits.
The conversion tracking stack at a glance
4 + 1
Meta CAPI + Google Ads server-side + GA4 + GTM Server-Side layer
4 tiers
Value-tier events: admit / VOB / scheduled / qualified inquiry
6-10 wk
Build timeline from decision to reconciliation-clean stack
$8-18K
One-time build + $200-500/mo container hosting
GA4 as the cross-channel measurement layer
GA4 is not the source of truth for conversion signal. GA4 is the cross-channel measurement layer that tells you which channels are producing which conversions. The source of truth is always the CRM.
The specific configuration that makes GA4 work in a HIPAA-safe stack.
Custom events for each value tier. GA4 receives neutral custom conversion events (tier_1_conversion through tier_4_conversion, mapped to admit, VOB, scheduled, and qualified inquiry inside the CRM) via the server-side container. Each event carries the value field. The events fire from server-side, not client-side, which keeps PHI out of the GA4 pixel.
No PHI in event parameters. Event parameters can include the value tier, the source channel, and the campaign identifier. Event parameters cannot include the patient’s condition, the LOC they scheduled for, or any identifier that could de-anonymize the individual patient.
Custom dimensions for source attribution. GA4 supports custom dimensions that carry source data (utm_source, utm_medium, utm_campaign) through to conversion events. Configure custom dimensions for the specific source attribution the facility uses in reporting. Without this configuration, GA4 conversion events lose source attribution beyond the first-touch session.
Server-side pageview. Client-side GA4 pageviews are acceptable for standard analytics use, but any pageview on a thank-you page, confirmation page, or PHI-adjacent URL should be routed through the server-side container to strip PHI before it reaches GA4.
The GA4 configuration is the layer where most facilities have the largest gap between what they think their measurement is telling them and what it actually is.
The double-counting problem
The measurement gap I see most often looks like this: GA4 credits organic with a batch of conversions, Google Ads credits paid with another, and the two together add up to more admits than the CRM shows for the same period. The two attribution platforms are double-counting because the conversion event is defined differently in each, and nobody at the facility has reconciled the two definitions against the CRM as source of truth. The organic side and the paid side both look like they are winning until you add them up and the total is bigger than the actual admit count.
Trevor Gage, Director of Marketing
Set up CallRail in HIPAA-enabled mode
CallRail is the standard call tracking platform for treatment center marketing. It can be configured for HIPAA compliance. It is not configured that way by default.
The setup steps are specific. Sign a BAA with CallRail before activating the account.
Enable the HIPAA-compliant feature set in the account settings, which restricts data retention and modifies how call recordings are stored. If the program is recording intake calls, the recordings must live on a HIPAA-enabled plan with BAA coverage.
Install CallRail’s Dynamic Number Insertion via Google Tag Manager. DNI swaps the displayed phone number on the website based on the traffic source, which is what enables call attribution back to specific keywords and ads.
Without DNI, every call attributes to the same number and the keyword-level data is lost.
Configure CallRail to forward call events to the HIPAA-compliant analytics platform set up in Step 1. From there, the platform forwards the de-identified call event to Google Ads and GA4 as a conversion. The PHI never leaves CallRail’s BAA-covered infrastructure.
The key check: a call conversion firing into Google Ads should never carry the patient’s phone number, transcription content, or any free-text data from the call. The conversion is a count and a source, not the call itself.
Connect to Google Ads
The final step is wiring the de-identified conversion signal from the HIPAA-compliant platform into Google Ads.
Set up Google Ads conversion actions for each pathway: phone calls, form fills, chat starts, and any other conversion goal the program is tracking. Keep Google Ads enhanced conversions off. Google’s customer data policy says conversions related to health or medical information can’t be used for measurement in enhanced conversions, even when a HIPAA-compliant platform offers the setting.
Our HIPAA-safe conversion tracking stack walks the full server-side setup, and our Google Ads strategy guide for behavioral health providers covers how these conversion actions feed bidding. For the wider program they sit inside, see our behavioral health marketing guide.
Configure the conversion source as the HIPAA-compliant platform, not GA4 directly. This routing is what protects the program from PHI exposure into Google’s systems while still giving Google Ads enough conversion data to optimize against.
Set conversion attribution windows deliberately. Behavioral health decision cycles are longer than ecommerce cycles. A 30-day post-click window misses conversions that happen 35 to 60 days after the original ad. A 90-day window often captures the actual decision pattern. Coordinate the windows with the downstream conversion path so the campaign optimization sees the full picture.
Verify conversion accuracy weekly for the first 60 days after launch. Compare Google Ads conversion counts against CRM admit counts. Discrepancies of more than 10% to 15% indicate a tracking gap that needs investigation.
How Profound Treatment drove 31 admits and a 42% drop in cost per viable in one quarter
Broad match pivot, negative keyword management, and intake-level conversion tracking turned a fragmented paid strategy into a predictable admissions engine.
Read the case study →68 viable VOBs at $4,529 cost per viable
Frequently asked questions about HIPAA-compliant Meta CAPI
Will switching to CAPI hurt our ad performance versus the pixel?
When set up correctly, CAPI typically improves performance because it captures conversion data that the browser pixel misses (cookie blockers, iOS 14+ tracking limits, third-party cookie restrictions). The performance dip operators see is usually from a botched implementation, not from CAPI itself.
The most common cause of performance loss is incomplete event match quality. CAPI without proper user identifier hashing produces low Event Match Quality scores, which Meta uses to weight conversion attribution. Low EMQ means Meta cannot tie conversions to specific impressions, which hurts campaign optimization.
A properly built HIPAA-compliant CAPI implementation usually recovers once Meta’s algorithm learns from the cleaner conversion signal. Benchmark cost-per-admit before and after the migration on your own account rather than relying on a promised lift.
Can we still use Meta audiences if we’re HIPAA compliant?
Yes, with significant constraints. Lookalike audiences built from non-PHI signals (website visitor behavior on non-condition pages, ad engagement, video view duration) are fully usable. Custom audiences built from patient data (admission lists, CRM lead lists, prescriber contact lists) cannot be used, even hashed.
The distinction is whether the audience definition itself implies PHI. A custom audience labeled ‘admitted patients’ is PHI even if uploaded as hashed emails, because the audience membership reveals condition status. A lookalike of ‘all website visitors’ is not PHI because membership reveals nothing about treatment.
Most non-compliant treatment center accounts we audit have at least one Custom Audience that crosses this line. The cleanup is usually straightforward: delete the offending audiences, rebuild lookalikes from compliant seed audiences, and document the change for compliance review.
Do we need a BAA with our analytics intermediary vendor?
Yes. Any vendor that handles patient data on behalf of your treatment center needs a signed Business Associate Agreement before they touch the data. This includes analytics platforms (Freshpaint, Segment with healthcare config, Adobe Healthcare), call tracking platforms (CallRail with HIPAA mode, Invoca), and any CRM that receives form submissions from your site.
Vendors that refuse to sign a BAA or charge a significant premium for one are signaling something. The standard for HIPAA-aware vendors is a BAA included in the enterprise pricing tier. Vendors that treat the BAA as a custom request or compliance exception are unlikely to have the infrastructure to actually comply.
The BAA itself is the first checkpoint, not the last. The vendor also needs documented technical safeguards (encryption in transit and at rest, access logging, breach notification procedures). The BAA confirms the legal commitment; the technical documentation confirms the operational capability.
What if our current Meta setup is non-compliant?
The cleanest path is a phased migration that does not turn off paid social during the rebuild. Phase one removes the offending pixel from PHI-collecting pages and disables non-compliant Custom Audiences. Phase two builds the HIPAA-compliant analytics intermediary. Phase three switches conversion tracking to server-side CAPI through that intermediary. Phase four rebuilds compliant lookalikes from clean seed data.
Plan the migration in phases rather than as a single cutover. We do not recommend the rip-and-replace approach. Pulling the pixel without a compliant tracking layer in place leaves the account blind to conversions and starves Meta’s algorithm of optimization signal during the transition.
The expensive mistake is to delay the migration because the current setup is producing acceptable performance. HIPAA enforcement does not wait for performance gaps. The penalties for a compliance failure caught by an audit or a patient complaint usually exceed the cost of the migration by an order of magnitude.
How long does proper HIPAA CAPI setup take?
A clean HIPAA-compliant CAPI setup from scratch typically takes 4 to 8 weeks for a treatment center. The variability depends on the analytics intermediary choice, CRM integration complexity, and how cleanly the website’s existing tracking can be deconstructed. New programs starting from zero move faster than legacy programs with years of pixel and audience accumulation.
The work splits into discrete blocks. Selecting and contracting with the intermediary takes 1 to 2 weeks. Configuring server-side event forwarding takes 1 to 2 weeks. Auditing and removing existing non-compliant audiences takes 1 to 2 weeks. Verification and EMQ tuning takes 1 to 2 weeks.
The hidden cost is documentation. The HIPAA compliance value of the work depends on being able to demonstrate to an auditor what was changed, when, and why. We build the documentation alongside the implementation rather than scrambling for it after a complaint or audit lands.
The perspective in this article comes from 9 years working exclusively inside behavioral health.
We are a team built by people in recovery who understand that behind every admission is someone asking for help. If that resonates, get to know us.
Mitch Marowitz is the Director of Paid Admissions at Webserv. Webserv works with behavioral health and addiction treatment centers on SEO, paid media, and full-funnel admissions strategy.